

RSA Authenticator (SecurID)
3.3

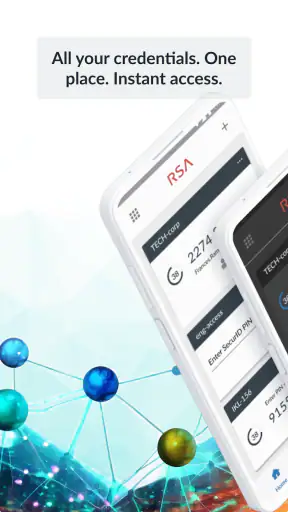
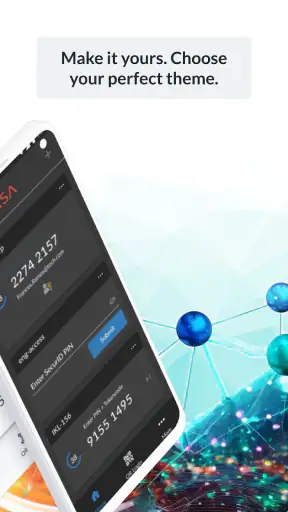
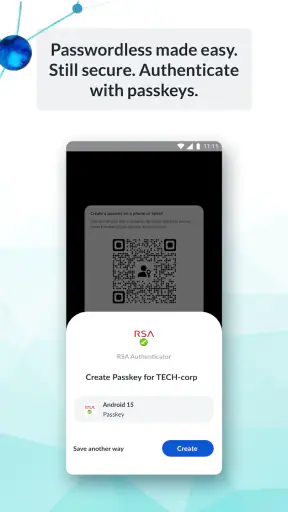
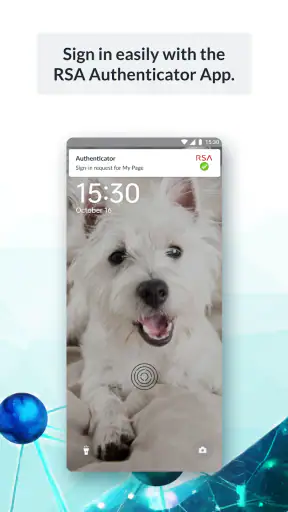
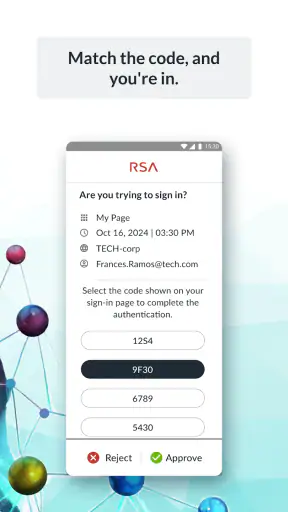
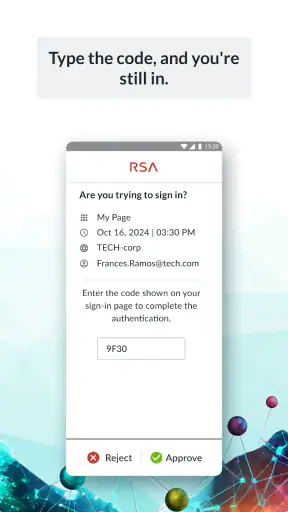
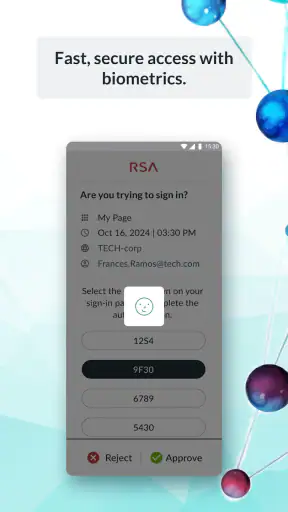
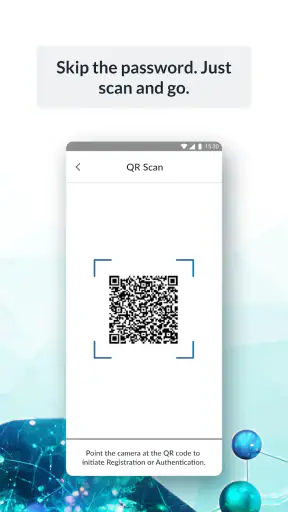
When I need a second layer of protection for a work account, I want the approval step to be quick, clear, and dependable rather than clever. RSA Authenticator (SecurID) is built for that focused job. It is a communication app from RSA Security, available free of charge, and its purpose is to help users authenticate with options such as passkeys, biometrics, one-time passwords, and other sign-in methods. After spending time with it, my view is straightforward: it is a practical security companion for people whose organization already uses RSA authentication, but it is not an all-purpose replacement for every authenticator app.
The most important point is that this is not an app I would choose simply because I wanted a general password manager or a universal identity wallet. Its value depends heavily on the account or service you are trying to access. In the right workplace setup, it can make a protected login feel routine. Outside that environment, the setup process and service compatibility matter much more than the attractive promise of several authentication choices.
How RSA Authenticator fits into everyday sign-in
The app sits between you and a protected service. Instead of relying only on a password, you use an additional method to prove that you are the person signing in. Depending on how the account has been configured, that may involve a passkey, a biometric check, or a one-time password. I like this role because it keeps the app’s purpose narrow: it is there when access needs verification, and it does not try to become a social platform, messaging tool, or sprawling account dashboard.
That narrow focus also explains why the experience can feel different from consumer-oriented authenticator apps. A workplace administrator may control enrollment, the available authentication methods, and the recovery process. From the user’s point of view, the app may look simple, but the surrounding account setup determines whether it feels effortless or awkward. If your employer or service has already told you to use RSA Authenticator, that is a strong reason to install it. If you are selecting an authenticator independently, compatibility should be your first question.
The app has been available since May 24, 2011, and the current version is 4.7.1.1. It supports devices running operating system version 10 or later. Those details matter when an older phone is still in daily use, especially in organizations where employees keep a device for several years. I would check the phone’s system version before planning a rollout, rather than discovering the requirement during enrollment.
Its store presence is substantial, with more than ten million installs and an average rating of 3.3 from roughly eighteen thousand ratings. I read that combination as a sign of a widely used but not universally loved utility. Authentication apps often receive criticism when enrollment fails, a code is rejected, or a user changes phones, so the rating alone does not tell the whole story. Still, it is a useful reminder that security tools are judged by their difficult moments, not only by the normal sign-in.
What feels strongest in actual use
The best part is the range of authentication methods. A one-time password remains useful when a sign-in screen does not support a smoother approval flow, while biometrics can reduce the effort of confirming access on a compatible device. Passkeys are especially appealing for users who want to move away from repeatedly typing passwords. Having these approaches within the same security workflow gives an organization more flexibility than forcing every person into one method.
I also appreciate the practical distinction between convenience and assurance. A biometric prompt can be fast, but it still depends on the device and the way the account has been enrolled. A one-time password is less elegant, yet it can be a valuable fallback when a familiar approval path is unavailable. I would not treat one method as automatically superior in every situation. The useful choice is the one that works reliably for the particular account, phone, and sign-in environment.
A realistic example is a remote employee opening a company portal from home. The employee enters the usual account details, then completes the additional check in RSA Authenticator. On a normal day, a biometric confirmation may take only a moment. If the portal instead requests an OTP, the user can switch to the code-based route rather than being blocked by a single failed method. That flexibility is more meaningful than a long feature list because it addresses the small interruptions that make secure access frustrating.
Another strength is the app’s suitability for managed environments. RSA Security is a recognizable name in enterprise authentication, and the app makes more sense when it is part of an organization’s existing identity process. In that setting, the administrator can establish the expected route and users can concentrate on completing the check. I would rather use a focused tool designed for that relationship than an app that offers many unrelated features but gives little guidance about how it fits into company access.
There is also a useful habit hidden in the way these methods work: keep a recovery plan in mind before you need it. If a phone is lost, replaced, reset, or unavailable, the authentication app may no longer be the easy part of the process. I recommend asking the account administrator what the approved recovery route is while access still works. That is not a glamorous feature, but it is one of the most important practical steps when an authentication tool protects work systems.
Where the experience can become frustrating
The main weakness is dependency on enrollment and administration. Installing the app is only one part of the job. The account must recognize the device or authentication method, and the service must be configured to accept the route you are trying to use. When that chain is not prepared correctly, the app can appear unhelpful even though the real problem is somewhere else in the sign-in setup.
This is why I would not recommend treating it like a standalone download that solves security immediately. A person who installs it without instructions may still need an activation step, an account invitation, or assistance from an organization’s support team. The app is strongest when the surrounding process is clear. It is less satisfying for someone who expects to open it, scan any account, and manage all their logins without further guidance.
Recovery is another friction point. Authentication is deliberately designed to prevent easy access from an unrecognized device, so moving to a new phone can require more planning than moving an ordinary app. Before deleting the app from an old device, I would confirm that the new device has been enrolled and that the account’s fallback method works. I would also avoid assuming that a backup of the phone automatically guarantees a working authentication setup. The safe procedure is the one provided by the service or administrator controlling the account.
There is a human-factor issue as well. Offering passkeys, biometrics, and OTPs is useful, but multiple methods can make a first-time user wonder which one to select. In a company environment, unclear instructions can lead to repeated attempts, locked accounts, or unnecessary support requests. My advice is to follow the enrollment instructions exactly, test the chosen method while the old sign-in route is still available, and save the support contact somewhere outside the protected account.
The rating of 3.3 suggests that some users encounter enough friction to affect their overall impression. I would not dismiss the app because of that figure, but I would take it seriously when planning use across a large group. A security tool has to work for people who are not technically confident, including those using older phones, changing networks, or signing in under time pressure. Clear onboarding from the organization is almost as important as the app itself.
Useful habits that make it more dependable
My first recommendation is to enroll and test before the moment of urgency. Do not wait until a deadline, a business trip, or an emergency login to discover that the device is not recognized. Complete a normal sign-in, try the available verification method, and make sure you understand what the screen is asking you to approve. That small rehearsal can expose an account problem while help is still easy to reach.
Second, separate the phone problem from the account problem. If a code is rejected, check that you are using the current code and that you are signing in to the intended account before repeatedly trying. If a biometric prompt does not appear, use the alternate method that the organization has enabled rather than assuming the entire account is broken. This approach reduces the risk of turning a temporary issue into a lockout.
Third, think carefully before choosing convenience as the only criterion. Biometrics may be the fastest daily option, but an OTP can be valuable when the phone’s biometric sensor is unavailable or a different sign-in screen is being used. Passkeys may reduce password exposure, yet they still depend on the account and device arrangement. I see the best workflow as a primary method plus a known fallback, not a blind commitment to whichever option looks quickest during setup.
Finally, treat device changes as a planned security event. If you are upgrading phones, keep the old device available until the new one has completed enrollment and a real login has succeeded. If the device has already been lost, contact the account administrator or service support instead of trying random recovery steps. The inconvenience is real, but it is preferable to weakening the protection around a sensitive account.
Who should use it, and who should look elsewhere
RSA Authenticator is a strong fit for employees, contractors, students, or customers whose organization specifically supports RSA Security authentication. It is also suitable for people who value having more than one verification style, particularly those who want a biometric or passkey-based daily experience with an OTP option available when circumstances change. The free price removes a direct cost barrier, and the Everyone age classification makes it broadly accessible from an age-rating perspective.
I would be more cautious about recommending it to someone choosing a personal authenticator without any RSA-related requirement. If the services you use already support another authenticator and provide simple QR-based enrollment, a more general-purpose option may be easier. Likewise, people who want password storage, secure notes, family sharing, or a single place for many unrelated accounts should look at a password manager rather than expecting this app to fill that role.
It may also be a poor fit for users who regularly replace phones but do not have dependable access to account support. The security model is not designed around casual device swapping. That is a reasonable trade-off for protected access, but it means the app rewards preparation. For a personal account with a simple recovery process, another authenticator may feel less demanding; for a managed account where RSA is required, alternatives may not be accepted at all.
Compared with a basic OTP-only authenticator, RSA Authenticator offers a broader set of sign-in approaches, which can improve convenience when the account supports them. Compared with a password manager, it is narrower and more focused on proving identity during access rather than storing credentials. Compared with built-in device sign-in tools, it may be the better choice when an organization has standardized on RSA, but the built-in option could feel more natural for a personal service that already supports it. The right comparison is therefore not “which app has the most features?” but “which tool matches the account’s authentication system?”
My final recommendation
After weighing the smooth daily checks against the setup and recovery friction, I see RSA Authenticator as a specialized tool that does its best work inside a defined security environment. Its support for passkeys, biometrics, OTPs, and other authentication methods gives it useful flexibility, while its connection to RSA Security makes it especially relevant for managed access. The experience is not universally effortless, and the modest average rating reflects why careful enrollment and support guidance matter.
I would recommend it to anyone whose employer or service directs them to use it, with one condition: set up the fallback and recovery process before you need it. I would not choose it blindly as my personal all-purpose authenticator if the account does not depend on RSA’s system. For the right user, however, it turns an unavoidable security step into a manageable part of the daily routine. That is a worthwhile result, even if the app’s value comes more from dependable integration than from a polished, independent user experience.
My verdict: choose RSA Authenticator when your account already belongs to the RSA ecosystem or when you specifically need its combination of passkeys, biometrics, and one-time passwords. Skip it as a general-purpose security app if you need broad personal account management, effortless phone migration, or features beyond authentication.
3.3
1.18K Reviews
Pros
- Generates secure one-time codes for protected account logins.
- Supports push authentication for faster approval when enabled.
- Works with enterprise RSA SecurID authentication environments.
- Compact interface makes code access quick and straightforward.
- Adds an extra security layer beyond usernames and passwords.
Cons
- Requires an organization-issued registration or activation code.
- Some features depend on your employer’s RSA server configuration.
- Changing or losing phones may require administrator assistance.
- Push approvals need internet access and device notifications enabled.
- Less useful for personal accounts without RSA SecurID support.


